
Technical architecture of AccessPoint 2.6.0 for IT and security teams: the Microsoft 365 and hosted editions, components, identity, data residency, network and firewall rules, e-mail, zero-trust alignment, security advisories and shared deployments
Last updated: November 10, 2026 by Steve
Technical Architecture
This document provides a technical overview of the AccessPoint platform for solution architects, cybersecurity engineers, and IT directors evaluating the product for their organization. It is drawn from the AccessPoint Solution Architecture Guide (v2.6.0).
Platform Overview
AccessPoint is an access-to-information and privacy management platform built on Microsoft 365 and Azure. It began as a subject access request (SAR) management tool and has grown into an integrated ATIP/privacy office suite covering the full request lifecycle and the surrounding privacy program.
It comes in two editions that run the same code:
- AccessPoint for Microsoft 365 runs entirely within your organization's own Microsoft 365 tenant and Azure subscription: there are no external servers, databases, or third-party cloud dependencies at runtime, and all data remains in your environment under your control. Document conversion, viewing, editing and redaction burn-in run on AccessPoint's own document engine, inside your subscription. Most of this page describes this edition.
- Hosted AccessPoint (new in 2.6.0) is the same software run by Realizer in Canada at
app.realizer.io. People sign in with a Microsoft account and use it in the browser, with no Azure subscription, SharePoint or Teams to set up. Realizer holds the organization's data as its service provider. See Hosted AccessPoint.
The platform is organized into modules that share a single identity, RBAC, notification, audit, and reporting spine:
- Access requests — ATI/FOIA/GDPR intake, custodian tasking, document review and redaction, response packaging, and statutory reporting. Since 2.6.0 a request is answered in numbered releases (Release 1, 2 … and the final release), each recording exactly which records went out, at which redaction state and page numbers, with which letter and delivery; a release can carry its own fee instalment and be held until it is paid
- Video and audio records — recordings reviewed in the same document workspace: resumable uploads up to 50 GB, transcripts and captions, time-based redaction (box, blur, pixelate, mute, bleep, distort voice, withhold) with an exemption on every mark, in-tenant face detection and tracking, and burned MP4/MP3 release copies with a hash manifest
- Privacy assessments and audits — a configurable PIA/AIA/Security assessment engine with DPIA validation where a template configures it; privacy audits and regulator reviews run on the same engine
- Privacy incidents and breaches — intake, containment, risk-of-harm, and breach-notification workflows
- Complaints and appeals — complaint lifecycle with parties, statutory clocks, and investigation
- Privacy risk register — ISO 31000-style risks, treatment plans, and key risk indicators
- Privacy program — one hub for the inventory of programs, systems and vendors, GDPR Article 30 records of processing (ROPA) with register export, readiness by law, attestations and discovery surveys
- Commitments register — tracked privacy commitments with cadence and check-ins
- Public intake portal (optional) — an internet-facing web app for online requests, complaints and incident reports, status tracking, secure delivery of responses, a reading room and online fee payment through the institution's payment provider
- Repository connectors (optional) — browse, search and capture records from systems outside Microsoft 365 into any documents workspace, with provenance
- Accessible editions (optional) — accessible versions of response packages with a PDF/UA check
- Case archiving — storage policies that move closed cases' files to cooler storage tiers, preservation holds and a disposition log
- Lab mode (called train mode before 2.6.0) — a training copy of the tenant with fictional cases, guided learning, learning paths and team exercises, kept apart from production. Since 2.6.0 the people around the trainee — requestors, third parties, custodians, reviewers, the senior official and others — can answer by script as simulated people who exist only in the training copy
- AccessPoint Learning (2.6.0) — in-product training inside your own AccessPoint: a How we decide coach beside the decisions people make on a case, with your organization's own coach notes; learning paths of modules; modules your organization writes in the Studio; checks, decisions and certificates; and completion records with reminders. Learning is part of the core product; writing your own modules, checks and certificates is a licensed module
- AI Assist (optional) — Azure OpenAI-backed suggestions and drafting: document summaries, AI redaction suggestions, grounded drafting, intake triage, assessment answer prefill, semantic search and duplicate detection, a statute-aware per-case assistant (Ask AccessPoint — clickable citations, saved conversations, a My-caseload mode), "Ask AccessPoint" data answers, a jurisdiction playbook that grounds process answers, auto-translation, and a daily brief — all opt-in per tenant, metadata-only logged, with per-record AI activity disclosure. In AccessPoint for Microsoft 365 it runs on an Azure OpenAI resource in your own subscription; in Hosted AccessPoint it stays off until an Administrator allows it (see AI processing and consent)
All modules are jurisdiction-pack driven, with no static seed data.
Two Editions
| AccessPoint for Microsoft 365 | Hosted AccessPoint (2.6.0) | |
|---|---|---|
| Where it runs | Your own Azure subscription and Microsoft 365 tenant | Realizer's Canadian service (Canada Central), at app.realizer.io |
| Front end | The SharePoint Framework web part in SharePoint Online and the Teams personal app | A browser app served by a web host on the same origin as its API |
| Sign-in | Microsoft Entra ID in your own tenant, with your MFA and Conditional Access | A Microsoft work, school or personal account; access comes from membership of an organization, by invitation |
| Tenancy | One deployment per customer, or a shared-services deployment serving several Microsoft 365 tenants | Many organizations in one database, kept apart by the application's tenant filter and SQL Server row-level security |
| Your own Exchange Online, through Microsoft Graph | Azure Communication Services from Realizer's sending domain, with your organization's confirmed Reply-To | |
| Microsoft 365 features | Record capture, Teams notifications, directory reconciliation, group-based roles | Not available |
| Updates | You deploy each release when you are ready | Realizer releases each version to the service |
| Who operates it | You (Realizer has no runtime access) | Realizer |
Key characteristics:
- Tenant-native (Microsoft 365 edition) — deploys as a SharePoint Framework (SPFx) solution and Azure PaaS services within your existing tenant
- No Power Platform dependencies — no Dataverse, Power Automate, or Power Apps licensing required
- Data sovereignty — in the Microsoft 365 edition all data resides in your Azure tenant's configured geography; in Hosted AccessPoint it resides in Realizer's Canadian service, kept apart per organization
- No vendor runtime access (Microsoft 365 edition) — the publisher cannot access your data during normal operation
- Flat-rate licensing (Microsoft 365 edition) — priced by the covered population of the organizations whose records are processed, with unlimited users and no per-user metering; the AI Assist, public portal, media, repository connector and AccessPoint Learning authoring modules are named in the signed license. Hosted AccessPoint is sold as per-organization plans
- A lapsed license is read-only, not a lock-out (2.6.0) — reading, search, reports, exports and Lab mode keep working; changes are refused until the subscription is renewed, and nothing is deleted
- Own document engine — conversion, viewing, editing and redaction burn-in run on AccessPoint's own native document engine; a document worker in your subscription handles Office, HTML and e-mail conversion, and the viewer and editors are served from the API's own origin with nothing loaded from a CDN
- Shared services supported — one deployment can serve several Microsoft 365 tenants, each with its own license and its own data (see Several Organizations in One Deployment)
- Privacy by design — custodian and contributor roles are structurally walled off from requestor and data-subject PII
- Configuration over code — request types, exemption codes, and choice fields are data-driven
- Multilingual by design — a three-tier translation system supporting 11 languages
- Instants in UTC, calendar days in the user's zone — every timestamp is stored as a UTC instant, but statutory calendar facts (received date, due date, overdue, days remaining) are computed on the caller's local calendar from the time zone the web part sends with each request
Architecture Diagram
The diagram shows AccessPoint for Microsoft 365. Hosted AccessPoint's is under Hosted AccessPoint.
Customer's Microsoft 365 Tenant          Customer's Azure Subscription
┌──────────────────────────────┐         ┌────────────────────────────────────────────┐
│                              │         │                                            │
│  SPFx Web Part               │         │  Azure App Service (Linux)                 │
│  (SharePoint Online /        │──HTTPS──│  ASP.NET Core 10 Web API (TLS 1.3 min)     │
│   Teams Personal App /       │  (JWT)  │    ├─ Entra ID JWT validation              │
│   Teams Tab)                 │         │    ├─ Tenant guard + user upsert           │
│                              │         │    ├─ License (read-only lapse) + modules  │
│  Installed from AppSource,   │         │    ├─ Permission-based authorization       │
│  the install page or the     │         │    ├─ PII filter middleware                │
│  Tenant App Catalog          │         │    └─ AccessPoint document engine          │
│                              │         │       (redaction burn-in, verification,    │
│  SharePoint Tenant Storage   │         │       viewer and editors; no CDN)          │
│  (API URL override,          │         │                                            │
│   optional)                  │         │  Azure SQL Database (application schema    │
└──────────────────────────────┘         │    and a separate portal schema)           │
                                         │  Azure Blob Storage + Storage Queues       │
        Microsoft Graph API              │  Key Vault (wraps the key ring)            │
        ┌──────────────────────┐         │  Application Insights + Log Analytics      │
        │ API identity (app):  │◄────────│                                            │
        │  Mail.Send           │         │  Container Apps environment (shared)       │
        │  User.ReadBasic.All  │         │   ├─ Document worker (default on):         │
        │  User.Read.All       │         │   │   Office / HTML / e-mail → PDF         │
        │  GroupMember.Read.All│         │   ├─ (opt-in) Media job                    │
        │  TeamsAppInstall…    │         │   └─ (opt-in) Accessibility checker job    │
        │  Application.Read.All│         │                                            │
        │  AppCatalog.Read.All │         │  (opt-in) Public portal web app            │
        │  AiEnterprise…Read   │         │           (+ optional Front Door + WAF)    │
        │ Signed-in user       │         │  (opt-in) Azure AI Search · Azure OpenAI   │
        │ (delegated): mail,   │         │           Document Intelligence · Speech   │
        │  calendar, files,    │         │  (opt-in) Defender for Storage             │
        │  Teams, OneNote, …   │         │  (opt-in) Relay (Hybrid Connections)       │
        └──────────────────────┘         └──────────────────┬─────────────────────────┘
          ← M365 record capture                             │ HTTPS + managed-identity token
            (delegated + app-only                           │ (API to connector only)
             Copilot)                    ┌──────────────────┴──────────────────────┐
                                         │  Repository connectors (optional)       │
                                         │   built-in: Azure Blob, MCP, SQL view,  │
                                         │     CMIS                                │
                                         │   remote, in Azure or on-premises       │
                                         │     through Hybrid Connections: file    │
                                         │     share, OnBase, OpenText Content     │
                                         │     Server (GCdocs), Laserfiche, Axon   │
                                         └─────────────────────────────────────────┘
Component Inventory
The components of AccessPoint for Microsoft 365. Hosted AccessPoint runs the same API, database schema and user interface in Realizer's subscription (see Hosted AccessPoint).
| Component | Technology | Deployed To | Purpose |
|---|---|---|---|
| SPFx Web Part | TypeScript, React 18.3.1 (provided by SharePoint), Fluent UI 8, SPFx 1.24.1 | Customer SharePoint Online / Teams | The SharePoint and Teams host of the shared user interface: the web part, its property pane and the SharePoint sign-in, API discovery and package-update adapters |
| Shared UI package | TypeScript, React 18.3.1 and Fluent UI 8 | Bundled into the SharePoint package (and into the hosted edition's browser app) | Every screen of AccessPoint, written once behind one host interface; it contains no SharePoint or Teams code, so the same screens run in SharePoint, Teams and the hosted edition |
| Teams App | Teams manifest v1.19, version lockstep with the SPFx solution and ApiVersion.Current (stamped by CI) |
Customer Teams Admin Center | Personal app, configurable tab, activity feed notifications with deep linking |
| Web API | C# / ASP.NET Core 10, .NET 10 (about 200 controllers) | Customer Azure App Service (Linux) | Business logic, data access, and AccessPoint's own document engine (redaction burn-in, independent verification, composition, text extraction) |
| Database | SQL Server (DacPac) | Customer Azure SQL Database | Relational data store (356 tables, 5,741 fields); the application schema, plus a separate portal schema for the public portal. A database that holds more than one tenant also carries a SQL Server row-level security policy (2.6.0) |
| Blob Storage and Queues | Azure Blob Storage (documents, migration-staging and document-conversions containers; opt-in evidence, portal-staging and portal-deliveries) and Storage Queues for the workers |
Customer Azure Storage Account | Document files, converted PDFs, working-file versions, media renditions, response packages, the data-protection key ring and transient conversion jobs; OAuth-only with shared-key access disabled |
| Key Vault (default on) | Azure Key Vault (RBAC, soft delete, purge protection) with an RSA-3072 key | Customer Azure Subscription | Wraps every new data-protection key, which protects stored connector and payment-provider secrets and the portal mail key; the vault's audit log goes to Log Analytics |
| Document worker (default on) | A Container App running the publisher's code-only worker image, fed by a storage queue; no inbound endpoint | Customer Azure Subscription (Container Apps) | Converts Word, Excel, PowerPoint, HTML captures and e-mail to PDF outside the API host, with AccessPoint's own document engine; its identity reaches only the conversion container and queue, never the case documents, SQL or the API |
| Monitoring | Application Insights + Log Analytics | Customer Azure Subscription | Telemetry, diagnostics, alerting |
| AI Search (opt-in) | Azure AI Search | Customer Azure Subscription | Full-text document content search plus semantic vector search (documents + case index); provisioned only when deployAiSearch=true |
| Azure OpenAI (opt-in) | Azure OpenAI Service | Customer Azure Subscription | AI Assist — grounded drafting, suggestions, semantic search, case assistant (Ask AccessPoint); managed-identity auth (no API keys), provisioned only when AI Assist is deployed. Since 2.6.0 you choose the models at deployment: Realizer's recommended models, which move with each release (gpt-6-luna and gpt-6.1-sol in 2.6.0), or models you name; embeddings always use text-embedding-3-small |
| Document Intelligence (opt-in) | Azure AI Document Intelligence (prebuilt-read) | Customer Azure Subscription | OCR for image-only scans feeding content search, duplicate detection, summaries, and redaction suggestions, and on-screen text detection in sampled video frames; managed-identity auth, provisioned only when deployDocumentIntelligence=true |
| Azure AI Speech (opt-in) | Azure AI Speech (batch transcription, S0) | Customer Azure Subscription | Time-coded, speaker-labelled transcripts and captions for video and audio records; the account reads audio from the documents storage account through its own managed identity; provisioned only when deploySpeech=true |
| Defender for Storage (opt-in) | Microsoft Defender for Storage (on-upload malware scanning) | Customer Azure Subscription | Every upload is scanned; a flagged file can never be previewed, played, downloaded, or released; provisioned only when deployDefenderForStorage=true |
| Media executor (opt-in) | Two Storage Queues + an event-driven, scale-to-zero Container Apps Job in the shared Container Apps environment, running the publisher's media worker image (the same media core the API runs in-process) | Customer Azure Subscription | Playback preparation, face and on-screen-text detection sweeps, region tracking and release rendering off the App Service; the image is code only and can be mirrored into the customer's own registry; provisioned only when deployMediaProcessing=true. Without it the App Service processes recordings in-process |
| Accessibility checker (opt-in) | Two Storage Queues + an event-driven Container Apps Job | Customer Azure Subscription | Checks response packages against the PDF/UA-1 standard; without it no package can pass the check and no conformance is ever claimed; provisioned only when deployAccessibilityCheck=true |
| Public portal (opt-in) | A second Linux web app on the same App Service plan, with its own managed identity | Customer Azure Subscription | The internet-facing requestor surface: intake forms, status and messages, secure deliveries, the fee pay page and the reading room. It reads and writes only its own SQL schema and its own two containers, and talks to the API through database tables, never HTTP; provisioned only when deployPublicPortal=true |
| Azure Front Door (opt-in) | Front Door Standard or Premium with a web application firewall | Customer Azure Subscription | Managed TLS on the portal's custom domain, rate limits on anonymous routes and, on Premium, managed rule sets and bot protection, in front of the portal and optionally the API; each fronted web app accepts traffic only from the profile |
| Hybrid Connections (opt-in) | Azure Relay namespace plus one connection per on-premises host; a Hybrid Connection Manager on the customer's premises (outbound 443 only) | Customer Azure Subscription and an on-premises host | Lets the API reach on-premises connector hosts with no VPN or inbound firewall rule; the API's own TLS session rides inside the tunnel |
| Repository connectors (optional) | The AccessPoint Connector Protocol (OpenAPI) and a .NET SDK; built-in connectors (Azure Blob, MCP, SQL view, CMIS) and remote connectors for network file shares, Hyland OnBase, OpenText Content Server (GCdocs), Laserfiche and Axon Evidence | Inside the API (built-ins); customer Azure Subscription or premises (remote) | Browse, search and capture records into any documents workspace with provenance (source path, version, SHA-256) and whole-folder collection jobs; the API calls connectors with its managed-identity token over an allow-listed client |
What the Publisher Operates
| Service | Purpose |
|---|---|
| Realizer Platform | License validation (a signed license token carrying the licensed modules), the jurisdiction pack catalog, Teams notification relay (default mode), SPFx API-URL discovery, the Teams personal-tab router, the post-deployment Finish Setup page and the SharePoint package install page (which serves only verified release files and refuses any request carrying a token). Packs are served to each AccessPoint version in the form that version can import. No customer case data is transmitted. The same service is also Hosted AccessPoint's control plane, which no Microsoft 365 deployment calls |
| AppSource Listing | SPFx package distribution |
| Deployment template and release files | The Bicep/ARM template with its guided Deploy to Azure form, the deployment script, the API, portal, SharePoint, Teams and connector packages, SBOMs, SHA256SUMS and signatures. A version folder is written once and never overwritten. The Microsoft Marketplace listing carries the subscription and license only |
| Container Registry | Anonymous-pull registry serving the code-only document, media and accessibility worker images; customers can mirror them into their own registry |
| Teams App Package | Teams manifest distribution (sideload or org app store) |
| Hosted AccessPoint (2.6.0) | The hosted edition at app.realizer.io, which Realizer runs for the organizations that use it (see Hosted AccessPoint) |
| Marketing demo and Training Lab | Realizer's own services (demo.realizer.io, learn.realizer.io) that run AccessPoint's screens on a simulation with fictional data. Neither is ever connected to a customer deployment |
For AccessPoint for Microsoft 365, no customer case data is transmitted to or stored by any publisher-operated service. Hosted AccessPoint is the exception by design: there Realizer stores and processes the organization's data for it.
Functional Modules
All modules run inside the single Web API / SPFx web part and share one identity, RBAC, comment, notification, My Day, audit, hours, review-workflow, and reporting spine. Each is data-driven via Jurisdiction Packs.
| Module | Summary |
|---|---|
| Requests (ATIP/SAR) | Request intake → custodian tasking → collection → response. Configurable types, statuses, numbering, calendars, and SLAs. Rolling releases (2.6.0): every response package is built through a numbered release that records its records, their redaction state, page numbers, packages, letter and delivery; release schedules give the dates the requestor was told; corrected and supplemental releases; a release can carry its own fee instalment and be held until it is paid. |
| Documents & Redaction | Faceted document workspace shared by every case type: tags, folders, email families with extracted attachments, read tracking, saved views, decision-based duplicate detection, client-composed PDF viewer (Original / Redline / Redacted preview drawn from the redaction records over one base PDF), redaction pipeline with exemptions, per-mark label modes and XFDF round-trip, find & redact patterns, rule-based and AI redaction suggestions, prior-request redaction reuse, response packaging with letterhead merge. |
| Media records (optional processors) | Video and audio evidence in the document workspace: resumable chunked uploads, playback preparation (proxy, poster, thumbnail sprites, waveform), Azure AI Speech transcripts and captions, time-based marks (box, blur, pixelate, mute, bleep, distort voice, withhold) burned into released MP4/MP3 files, in-tenant face detection and region tracking, ZIP release with MANIFEST.sha256. Runs in-process on the App Service or, with deployMediaProcessing, in a Container Apps Job fed by Storage Queues; Defender for Storage scanning gates release when deployed. |
| Requestors / Contacts | First-class reusable requestor identity, intake flow control, frivolous-and-vexatious conduct workspace, fees & verification, merge; consultations; correspondence composer with PII firewall. |
| Privacy Assessments & Audits | Configurable PIA/AIA/Security engine: templates, screeners, section assignment, scoring/tiering, risk register, closure/regulator summaries; DPIA validation (opinions, decision, section evaluation, regulator consultations, risk maps) where a template configures it; privacy audits and regulator reviews on the same engine. |
| Privacy Incidents / Breach | Incident intake, containment, risk-of-harm, breach-notification rules by regime, remediation. |
| Complaints & Appeals | Complaint lifecycle: parties, statutory clocks, admissibility, investigation, representations review. |
| Risk & Commitments | ISO 31000 risk register with appetite, KRIs, and treatment tasks; commitments register with cadence and check-ins. |
| Privacy program | One hub: inventory of programs, systems and vendors with GDPR Article 30 records and register export, readiness by law, a year view of everything dated, discovery surveys and append-only senior-official attestations. |
| Public portal & Payments (optional) | Staged, human-triaged public intake for requests, complaints and incident reports; requestor messages; secure delivery of response packages; an optional reading room; online fee payment through redirect-only payment providers (Stripe, Paymentus or a hosted page), so card and bank details are entered on the provider's page and never in AccessPoint. |
| Repository connectors (optional) | Records from outside Microsoft 365 in every documents workspace, registered and tested in Settings > Connectors. |
| Case archiving | Storage policies for closed cases, restores, in-app preservation holds on every destructive path, a sent mark on response packages and release-only or metadata-only disposition with a never-purged log. |
| Training (Lab mode) | A training copy of the tenant with fictional cases, guided learning, learning paths, team exercises and worked examples; nothing in it is sent, delivered, paid, uploaded or captured. Since 2.6.0 the people around the trainee answer by script: outside parties are the case's own contacts, and colleagues are simulated people that exist only in the training copy, never sign in and hold no role. |
| AccessPoint Learning (2.6.0) | The How we decide coach at decision points (the configuration's description and legal reference, your coach notes and the packs' notes); learning paths and audience rules; My learning and the module player; modules written in the Studio as structured content, never HTML, whose files are never case documents; checks and decisions whose results the server decides; certificates with verification inside your organization, revocation and recertification; completion records kept 7 years by default (1–15). Every learning write happens in production only, never in Lab mode. |
| Accessible releases (optional checker) | Accessible editions of a response package (always a tagged PDF; HTML, text and Word on request) with a PDF/UA-1 check; conformance is claimed only when the checks pass and a person confirms. |
| Reviews | Configurable sequential/parallel review-and-approval engine reused across all case entities. |
| Reporting & Audit | Fixed reports, catalog-driven custom report builder (Report Studio dashboards), statistical annual reports, SLA/management dashboards, hash-chained audit ledger and court-ready case audit exports. |
| AI Assist (optional) | Azure OpenAI-backed suggestions and drafting: summaries, redaction suggestions, grounded drafting, intake triage, custodian suggestions, assessment prefill and consistency checks, semantic search and duplicates, a statute-aware case assistant — Ask AccessPoint (clickable citations, prepare-a-draft, saved conversations) — plus a My-caseload/portfolio assistant, a pack-seeded jurisdiction playbook, Ask AccessPoint reporting, daily brief and catch-up digest, risk portfolio and conduct analysis. Per-feature tenant toggles; metadata-only logging (the assistant may additionally save owner-private transcripts). |
| Configuration & Platform | Jurisdiction-pack import (the Universal Baseline and, since 2.6.0, Universal Learning — AccessPoint Learning's content — plus 145 jurisdiction packs, each a starting point built from public information about the legislation, not legal advice), tenant settings, custom and group-based roles, delegation, directory reconciliation, licensed modules, feature toggles, custom fields, 11-language translation tables. |
Deployment Model
AccessPoint for Microsoft 365 uses a split deployment model. The SPFx web part is installed into the tenant app catalog, the Teams app package is installed from AppSource or Teams Admin Center, and the Azure backend is deployed into the customer's own subscription. There is no publisher-hosted backend for this edition: the customer owns every resource. An organization that does not want to run Azure resources uses Hosted AccessPoint instead, which Realizer operates.
The template creates a Premium v3 (P1v3) App Service plan by default. New subscriptions, and credit-based or sponsored ones, often have a Premium v3 quota of 0 in a region, and Azure then refuses the plan before anything else is created; request the quota first, or start on a smaller plan and scale up later (see the Deployment Guide). The backend is deployed by one of two methods:
- Guided Deploy to Azure form (recommended) — the Azure portal opens a four-page form (Basics, Features, Security and compliance, Advanced) that deploys the App Service, SQL, Blob Storage, Key Vault, the document worker and Application Insights, plus the optional public portal and Front Door, AI Search, Azure OpenAI, Document Intelligence, Azure AI Speech, Defender for Storage, media processing, accessibility checker, Hybrid Connections, private network and write-once evidence container options, via ARM/Bicep. The API package is deployed during the ARM deployment; code is downloaded once from the publisher CDN and stored in the customer's App Service, with no runtime external dependency. A required installation type choice guards redeploys: New installation creates the SQL server Entra-first (the deploying principal becomes the initial Entra admin, Entra-only auth from birth, so no SQL credential ever exists), while Upgrade existing installation preserves operator app settings, keeps customer-managed encryption keys and leaves database access untouched. The customer retains full ownership of the resource group.
- Bicep template + PowerShell script — for organizations with strict change control.
Deploy-AccessPoint.ps1deploys the infrastructure, re-asserts SQL Entra-only authentication, grants Microsoft Graph permissions to the managed identity (the scripted alternative to the Finish Setup page), configures the optional API-URL override and approves SPFx API permission requests. Each step can be skipped independently.
Graph permissions are normally granted through the publisher's Finish Setup page — the deployment emits a finishSetupUrl output that a customer Entra administrator opens to grant every managed-identity permission in one idempotent pass (re-run after upgrades to pick up new permissions). The SharePoint package is installed from the browser through an install page linked from the deployment's outputs: the administrator signs in to Microsoft 365, the page checks Realizer's signature on the package, and the administrator's browser installs it into the tenant app catalog with the administrator's own SharePoint rights. No package file is downloaded or uploaded by hand, and the Microsoft sign-in never leaves the administrator's browser. Later SharePoint package updates come from Settings > Setup > Update now through the same verified path.
Signed releases. Every release folder carries a SHA256SUMS manifest, detached signatures of the manifest and of every artifact, the publisher's public key and CycloneDX software bills of materials. A version folder is written once and never overwritten, and a version reaches the customer channel only through a manual approval plus evidence gates: functional tests, a security review, a bug review and release notes, and the penetration-test and performance gates whenever that evidence is filed. Every promoted release is tagged, and the release before the current one receives patches on its own release line; the latest channel only moves forward, so a patch to an older line never replaces the newest release. Signatures carry no transparency-log entry, so verification works offline. The deployment script verifies automatically, and its strict mode refuses unsigned material and installs exactly the verified packages.
The deployment is security-hardened by default: TLS 1.3, FTPS disabled, SCM/FTP basic authentication disabled, HTTP/2 enabled, Microsoft Defender for SQL on by default (opt-out), and a Key Vault wrapping the data-protection keys. Optional hardening includes a private network (service endpoints or private endpoints with public access turned off), Front Door with a web application firewall in front of the portal and the API, Defender for App Service, Defender for Storage malware scanning, a write-once evidence container, and customer-managed encryption keys for the documents storage account and the database. The API bundles its database DacPac and applies it on startup via a migration service (BlockOnPossibleDataLoss = true, DropObjectsNotInSource = false), so schema changes are additive and non-destructive. From 2.5.0 the database also records the version that last updated it, and an older API leaves a newer schema exactly as it is rather than rolling it back; the outcome is surfaced through /api/health. Post-deployment, an administrator grants consent for the Realizer enterprise app (Teams notifications), configures the sender mailbox, and imports a jurisdiction pack. On first sign-in AccessPoint imports the Universal Baseline and then Universal Learning by itself, in the background.
AI models (2.6.0). With AI Assist deployed, the deployment chooses the models of its two chat deployments: Recommended (Realizer's recommended models, which move with each release — gpt-6-luna for everyday work and gpt-6.1-sol for drafting and redaction analysis in 2.6.0) or Pinned (models you name, kept until you choose again). An upgrade keeps the installation's earlier choice unless you change it. Each model needs quota in the subscription for its AI region. Where the region does not offer the recommended models and no AI region is named, a new Azure OpenAI account is created in a region of the same geography that does; an existing account never moves, and pinned models or a named region are never remapped. Where AI inference is processed depends on the deployment type: the default global type keeps stored data in the account's region but may process inference in other Microsoft regions, and the data-zone type keeps it within the EU or US data zone.
Licensed Modules and a Lapsed License
A subscription always includes the core product: every case register, documents and redaction, reviews, correspondence, reports, jurisdiction packs, Lab mode and the learning half of AccessPoint Learning (the coach, learning paths, My learning and completion records). Premium modules — AI Assist, the public portal, media, repository connectors and, since 2.6.0, AccessPoint Learning authoring (the Studio's modules, audience rules, checks, decisions and certificates) — are named in the signed license. A module works only when it is licensed, deployed where it needs an Azure resource, and switched on; a downgrade never deletes data.
A lapsed license is read-only (2.6.0). Beyond its grace period, an expired license, or one Realizer revoked, makes the tenant read-only until the subscription is renewed, instead of blocking it. Reading, search, reports, exports, Lab mode and each person's own preferences keep working; every change is refused. E-mail and Teams notices are not sent (the in-app feed still records), the portal's intake closes, connectors and AI pause, and media processing waits. Nothing is deleted, and the next successful license check restores everything. Read-only never comes from a publisher outage: without a confirmation from Realizer the API keeps working for 30 days on its last validated license.
Authentication and Identity
AccessPoint uses Microsoft Entra ID as its sole identity provider. There are no application-specific user accounts or passwords. The SPFx web part acquires a JWT for the API audience via AadHttpClient; the API validates the issuer, audience, signature, and expiry on every request. MFA and Conditional Access policies configured in the tenant apply in full.
This section describes AccessPoint for Microsoft 365. Hosted AccessPoint signs people in through its own web host, with Realizer's app registration, and decides access by membership of an organization rather than by the token's tenant (see Sign-in, sessions and organizations); nothing here changes for a Microsoft 365 deployment.
User (Browser)                SharePoint Online           AccessPoint API
     │                              │                          │
     │  1. Load SPFx web part       │                          │
     │─────────────────────────────►│                          │
     │                              │                          │
     │  2. AadHttpClient.getClient()│                          │
     │  (SPFx acquires token for    │                          │
     │   api://<client-id> audience)│                          │
     │                              │                          │
     │  3. API call + Bearer token  │                          │
     │──────────────────────────────┼─────────────────────────►│
     │                              │                          │
     │                              │  4. Validate JWT:        │
     │                              │     - Issuer (Entra ID)  │
     │                              │     - Audience (api://)  │
     │                              │     - Signature          │
     │                              │     - Expiry             │
     │                              │                          │
     │                              │  5. UserUpsertMiddleware: │
     │                              │     Extract claims →     │
     │                              │     Upsert Users table   │
     │                              │                          │
     │                              │  6. PermissionService:   │
     │                              │     resolve roles +      │
     │                              │     permission grants    │
     │                              │                          │
     │     ◄── JSON response ───────┼──────────────────────────│
| Parameter | Value |
|---|---|
| Identity Provider | Microsoft Entra ID (Azure AD) |
| Protocol | OAuth 2.0 / OpenID Connect |
| Token Type | JWT Bearer |
| Audience | api://<client-id> and <client-id> (both v1 and v2 tokens accepted) |
| Issuer | Any Entra tenant's issuer — https://login.microsoftonline.com/{tenantId}/v2.0 (v2) and https://sts.windows.net/{tenantId}/ (v1) formats validated; the token's tid claim drives tenant scoping |
| App Registration | Publisher-operated multi-tenant app, consented per customer tenant (no per-customer app registration to manage or rotate); exposed scope access_as_user; no client secret. Isolation between customer tenants is enforced by the validated tid claim plus a license/subscription check |
Managed Identity
The App Service uses a system-assigned managed identity to authenticate to backend services, so no client secrets or certificates are stored in the application:
- Azure SQL Database — Entra-only authentication (the server is created Entra-first; no SQL credential ever exists)
- Azure Blob Storage —
DefaultAzureCredential(managed identity in production) - Microsoft Graph API —
ManagedIdentityCredentialwith application permissions - Azure Key Vault — the API identity may only wrap and unwrap with the one
dataprotectionkey, through a role assigned on the key rather than the vault - Optional resources (AI Search, Azure OpenAI, Document Intelligence, Azure AI Speech, the workers' Storage Queues) — managed-identity-only, with local/key auth disabled; the Speech account, the document worker, the media job, the accessibility job and the public portal each carry their own managed identity scoped to the containers, queues and schema they need (the workers never reach SQL or the API), and a customer-mirrored worker image is pulled with the worker's identity through an AcrPull grant
- Microsoft 365 in a different Entra tenant — the template attaches a second, user-assigned identity, and the API signs in to Microsoft 365 as a multitenant app registration that trusts that identity as a federated credential. No client secret exists and no license key is needed
Managed identity credentials are rotated automatically by Azure.
Authorization and RBAC
AccessPoint implements a granular, tenant-configurable permission model stored in Azure SQL and enforced at the API layer on every request: a product-defined catalog of atomic permission codes (e.g. request.modify, document.view, redaction.approve, request.view.pii) is grouped into roles, and every controller action is gated on a permission code.
| Role type | Roles | Notes |
|---|---|---|
| System role | Administrator (the only built-in standing role) | Resolves to every catalog permission — computed from the catalog, not database seeding — so it can never be locked out; immutable and undeletable. |
| Relationship roles | Reviewer, Custodian, Contributor, Reader, Advisor | Product-defined permission bundles conferred automatically and per-target by work/collaboration relationships (custodian assignment, contributor task, review, advisor/reader membership). Not directly assignable, scoped to the related record, and never include requestor PII. |
| Tenant roles | e.g. Request Coordinator (shipped via the Universal Baseline pack), plus any custom roles | Fully editable permission bundles managed in Settings > Roles & Permissions. Coordinator/officer roles are entirely tenant-defined — the pack-shipped Request Coordinator is the de-facto access-and-privacy-officer role. |
| Role | Sees Requestor PII | Typical Access | Typical User |
|---|---|---|---|
| Administrator | Yes | Everything (all catalog permissions) | IT admin, system owner |
| Request Coordinator (tenant role) | Yes | Manages requests, assignments, redactions, correspondence | Access & privacy officer |
| Reviewer | No | Read + flag/resolve redaction concerns on requests under review | Legal counsel, QA |
| Advisor | No | Read + view/flag redactions (never apply or approve) | Consulting counsel, SME |
| Custodian | No | Own assignments and their documents | Department records officer |
| Contributor | No | Own tasks and their documents | Subject matter expert |
| Reader | No | Read-only on associated requests and shared documents | Oversight, audit |
Enforcement points:
[RequirePermission(code)]attributes — a dynamic policy provider maps each controller action to a catalog permission codePermissionService— resolves the caller's effective permissions (standing roles unioned with per-target relationship grants), with object-scoped checks at request/document/assignment/task level- Resource-level ownership checks — e.g., a Contributor can only access their own tasks; a Custodian only their own assignments
PiiFilterMiddleware— strips requestor PII fields from JSON responses for any caller who does not hold the view-requestor-PII permission
All API write endpoints enforce permissions server-side at the controller level. Document reclassification is scope-aware — the user who collected a document is the one who can reclassify it — and once a request is closed, mutations on its object graph return HTTP 409, with a small set of deliberate exceptions (post-closure correspondence, retention purge, and reopen). Standing role assignments are scoped (global, request, assignment, or task), optionally time-limited, and relationship roles are never written as standing assignments — they are derived per-target from the underlying work records. The first user to access the system is bootstrapped with the Administrator role, and a server-side guard prevents removing the last active Administrator.
Data Residency and Sovereignty
This section describes AccessPoint for Microsoft 365, where every store is the customer's own. In Hosted AccessPoint the same kinds of data live in Realizer's Canadian service, kept apart per organization (see Where hosted data lives).
All stored data resides in the customer's Azure tenant in the region selected during deployment, and is not stored in other regions unless the customer explicitly configures Azure geo-replication. The processing exceptions to assess are the ones the customer chooses: AI Assist's default global deployment type (inference may be processed in other Microsoft regions), Azure Front Door (a global service) in front of the portal or the API, the Teams relay's default mode, and a payment provider.
Canadian federal departments: For GC-specific data-residency requirements, ITSG-33 control mapping, and the GC Cloud Guardrails mapping, see the GC Security Controls Reference.
Customer Data Locations
| Data Type | Storage Location | Controlled By |
|---|---|---|
| Request records, user data, audit trail | Azure SQL Database | Customer's Azure subscription |
| Uploaded documents, converted PDFs, and media renditions (playback proxies, transcripts, captions, released recordings) | Azure Blob Storage | Customer's Azure subscription |
| Application telemetry | Application Insights / Log Analytics | Customer's Azure subscription |
| SPFx web part assets | SharePoint CDN | Customer's M365 tenant |
| API URL override (optional) | SharePoint Tenant Storage Entity | Customer's M365 tenant (primary discovery is the publisher API-discovery endpoint) |
| AI search indexes, summaries, OCR output, transcript segments (opt-in) | Azure AI Search / Azure SQL | Customer's Azure subscription |
| Documents in conversion | A transient container and queue on the documents storage account; deleted as soon as the API has the result, with a one-day backstop. The queue message carries a job id, never a path or content | Customer's Azure subscription |
| Data-protection key-encryption key | Azure Key Vault | Customer's Azure subscription |
| Portal submissions, sessions (hashed), case projections, deliveries and requestor events (opt-in) | Azure SQL, the portal schema, the only schema the portal identity can reach; requestor e-mail addresses are encrypted with a public key whose private half only the API holds | Customer's Azure subscription |
| Requestor uploads before triage and copies of released packages (opt-in) | Azure Blob Storage (portal-staging, portal-deliveries) with lifecycle backstops |
Customer's Azure subscription |
| Lab mode cases, sessions and exercise records, simulated people and their scripted answers | The same database and storage under a separate training tenant id; fictional content only | Customer's Azure subscription |
| AccessPoint Learning modules, their files, attempts and completion records | Azure SQL; module files in Blob Storage under the tenant's own learning folder, never as case documents; certificates are rendered on request, not stored | Customer's Azure subscription |
| Card and bank details for fee payments (opt-in) | Never AccessPoint — entered on the payment provider's hosted page; AccessPoint stores the provider's transaction id, the amounts and the verified notification | The payment provider, under the customer's contract with it |
What Crosses Tenant Boundaries
| Data Flow | Direction | What Is Transmitted | Purpose |
|---|---|---|---|
| License validation | API → Publisher Platform | Entra token (the token's tid claim identifies the tenant), API version, and the API's own base URL (self-registration for web-part discovery) |
Validate active subscription; the response is a signed license token (licensed modules, security advisories) plus the latest published AccessPoint version so the Setup panel can show an "Update available" notice (no usage or case data) |
| Jurisdiction pack catalog and installation | API → Publisher Platform | Catalog and download requests (with the API's own version), then an installation record: tenant ID, pack, item types and the installing Administrator's Entra object ID | Import legislative configuration, served in the form that API version can import |
| SharePoint package install page | Administrator's browser → Publisher Platform, then browser → Microsoft sign-in and the tenant's SharePoint | To the publisher: the Microsoft 365 tenant ID, the SharePoint name and the version, in the link; the publisher returns only verified release files and refuses any request carrying a token | Install the SharePoint package; the sign-in and the install stay between the browser, Entra ID and SharePoint |
| API-URL discovery | SPFx → Publisher Platform | Bearer token (tenant ID claim only) | Resolve the customer API base URL when no storage-entity override is set |
| API → Microsoft Graph → your Exchange Online | Email content via Mail.Send |
Notifications, portal codes and advisory notices from the shared sender mailbox; correspondence and automatic acknowledgements from the mailbox chosen for the letter (the officer's own, an intake mailbox or the shared sender). See Email Through Exchange Online | |
| Teams notifications (optional — toggleable / eliminable) | API → Publisher Platform → Microsoft Graph | Activity type, recipient + tenant GUIDs, notification title/preview text, acting-user name, request number, record id (deep link) | Send Teams activity feed notifications (proxied through the publisher's multi-tenant enterprise app because sendActivityNotification must be called by the app that owns the Teams manifest). This is the only notification channel that leaves the tenant — email and the in-app feed deliver the same notices in-tenant. See Teams Notification Data Sharing |
| User profile lookup | SPFx → Microsoft Graph | User search queries | People picker, user resolution |
| Worker image pull (default images only) | Customer Container Apps → Publisher container registry | Image tag or digest, egress IP, time — code only, no customer data | Start the document worker and the optional media and accessibility workers; eliminated by mirroring the images into the customer's own registry |
| Fee payment session (optional) | API → payment provider (Stripe, Paymentus or the configured processor) | Amount and currency, a short payment reference, the request number in the description and return and notify URLs. Stripe also receives the requestor's e-mail address; Paymentus receives no name or e-mail; no provider receives the requestor's name from AccessPoint | Open the provider's hosted page; confirm, refund and reconcile payments |
| Payment notification (optional) | Payment provider → portal | The provider's webhook, verified by the API; an unsigned one only triggers a status query | Confirm a payment server-side; a browser return never marks anything paid |
| Requestor traffic (optional) | Requestor → portal (optionally through Azure Front Door) → provider hosted page | The requestor's own answers, uploads and code entries | Public intake, tracking, download and payment |
| Repository connector calls (optional) | API → connector hosts the customer operates (in Azure or on premises) | Browse, search and capture calls with the API's managed-identity token | Capture records from outside Microsoft 365; the publisher never sees this traffic |
What Never Leaves the Tenant
- Request records and requestor PII
- Uploaded documents, recordings, transcripts, and released copies
- Audit history
- Configuration data (request types, templates, numbering)
- Role assignments
- Document conversion and media processing — all of it runs in the customer's App Service or Container Apps; the only outbound request a conversion makes is the download of an e-mail's remote images (at most 25 per message, public addresses only)
- Repository connector traffic, and everything the public portal holds — the publisher hosts nothing for the portal, and the portal never calls the publisher
- AI Assist prompts and responses — when AI Assist is deployed, the Azure OpenAI resource runs in the customer's own subscription, and data at rest stays in its region (with the default global deployment type, Microsoft may process inference in its other regions); Microsoft does not train models on the content, and prompt/response content is not stored (only usage metadata, for the budget meter and the case audit export's AI-involvement disclosure). Nothing is sent to the publisher
- In-app and email/Outlook notifications — the in-app feed is served from the customer's own API; email is sent from the customer's own mailboxes via
Mail.Send. Neither transits the publisher. Only the optional Teams activity feed sends any data outside the tenant, and even that can be minimised or eliminated (below)
Teams Notification Data Sharing (Optional)
Consistent with the data-sovereignty promise, the only tenant data that leaves the boundary for notifications is an optional Teams activity payload — and it can be minimised or removed entirely. Every notification is delivered on up to three channels; two are always in-tenant (the in-app feed, served from the customer's API, and email/Outlook, sent from the customer's own mailbox through its own Exchange Online). The Teams activity feed is a convenience: in its default mode the customer API POSTs a small payload to the publisher's multi-tenant app, which calls Graph sendActivityNotification (which must be invoked by the app that owns the Teams manifest). The publisher stores none of it and logs only the recipient + tenant GUIDs.
Fields in the default (publisher-relay) Teams payload — and what the Minimise toggle strips:
| Field | Contains | Personal data? | Removed by Minimise? |
|---|---|---|---|
tenantId / recipientUserId |
Tenant + recipient Entra GUIDs | No — identifiers | No (routing) |
activityType |
Fixed manifest enum (e.g. assignmentCreated) |
No | No |
previewText / topicText |
Preview + title (assignment/task name, notification text) | Potentially (free text) | Yes → placeholder |
actorName |
Acting staff member's display name | Yes — personal name | Yes → "AccessPoint" |
requestNumber |
Request reference code | No — reference | No (context) |
relatedEntity + relatedRecordId |
Record type + GUID (deep link) | No — identifiers | No (deep link) |
Requestor PII is never in the payload — there is no requestor name/email field, and Custodian/Contributor notifications are PII-blanked upstream regardless. Two controls tighten this further:
- Minimise (
Notifications:TeamsMinimalPayload, a tenant toggle) replacespreviewText,topicText, andactorNamewith neutral placeholders, so names, titles, and free text never leave the tenant — only routing/deep-link identifiers do. No manifest change required. - Eliminate (
Notifications:TeamsRelayMode=Direct) makes the customer API call GraphsendActivityNotificationitself with its managed identity, so no payload reaches the publisher at all. It requires theTeamsActivity.Sendapp-role on the API's managed identity and the Teams manifest'swebApplicationInfo.idpointed at the customer's own app — see the Deployment Guide.
| Mode | Payload to publisher | PII / free text leaves tenant | Setup effort |
|---|---|---|---|
| Default relay | Yes (fields above) | Names/titles, unless minimised | None |
| Minimise toggle | Yes (identifiers only) | None | One toggle |
| Direct (self-hosted) relay | None | None | MI grant + manifest edit |
| Teams disabled | None | None (email + in-app only) | None |
Several Organizations in One Deployment
By default each customer deploys its own instance: a dedicated database, App Service and storage account, with the tenant ID from each user's validated token scoping every query. A deployment that serves one organization behaves exactly like that, and nothing below applies to it.
Since 2.5.0, one deployment — one set of Azure resources and one database — can also serve several Microsoft 365 tenants. This is the pattern for a shared-services team serving the departments of a government, or a provider serving client organizations.
- Shared services, separate data. Each served tenant keeps its own users, roles, settings, jurisdiction packs, cases, documents, training copy and license. Every record carries its tenant, an unconditional query filter scopes every read to the caller's tenant, and blob paths are prefixed with the tenant ID. The compute, database, storage, workers, AI and portal are shared, so they are sized for all tenants together.
- Each tenant on its own license. The deployment validates each tenant's license with a token issued in that tenant, so every organization needs its own subscription. An additional tenant is served only while its own license is valid and only while the Azure operator lists it.
- The list is an operator setting. The additional tenants are an App Service setting that only someone with Azure access to the App Service can change. No AccessPoint administrator of any tenant can add one.
- One Microsoft 365 identity per tenant. The deployment signs in to each tenant through the federated multitenant app registration, which exists in a tenant only once that tenant's administrator has consented it. That consent is the authorization. Email, Teams notices, directory search, group-based roles and Copilot capture all run in the tenant's own directory with its own identity, and never fall back to another tenant's connection.
- A tenant that is not ready fails alone. Until its administrator has consented the app, or while its license is missing or expired, its users are refused and nothing is written for them. The readiness check names each served tenant whose license or Microsoft 365 connection is not working.
- Each tenant installs its own front end. The SharePoint package, the Teams app and the notification mailbox live in the tenant's own Microsoft 365, and the web part finds the shared deployment's API by itself.
- Row-level security in the database (2.6.0). A database that holds more than one tenant gets a third line of defence under the application's tenant filter and its automated guard tests: a SQL Server row-level security policy on every tenant table, keyed on the tenant each connection carries, so a connection sees and writes only its own tenant's rows even if a query were written without the filter. It switches on by itself where the database is shared; an operator can run it in an audit mode first. Run a shared database with the least-privilege SQL runtime, so the API's own database user cannot alter or drop the policy — the health check reports Degraded until it does.
Hosted AccessPoint
Hosted AccessPoint (2.6.0) is AccessPoint as a service. An organization signs up at app.realizer.io, signs in with a Microsoft account and uses AccessPoint in the browser — no Azure subscription, no SharePoint and no installation. It is the same API, database schema and user interface as AccessPoint for Microsoft 365, started in its hosted mode, and Realizer operates it in a regional deployment in its own Azure subscription. The first region is Canada.
 Browser (Microsoft work, school or personal account)
   │ HTTPS 443
   ▼
 Azure Front Door + web application firewall — each site admits only Front Door
   │                       │                                     │
   │ app.realizer.io       │ ca.app.realizer.io                  │ api.ca.app.realizer.io
   ▼                       ▼                                     │ (viewer, editor, media
 Global entry: sends     Web host: Microsoft sign-in; tokens     │  and download links)
 each visit to the       kept on the server, never in the        │
 organization's region;  page's script                           │
 stores nothing            │ /api: the person's token + the organization chosen
                           ▼                                     ▼
                         AccessPoint API (hosted mode): membership check, a license per
                           │ organization, AccessPoint's own document engine
                           ├──► Azure SQL shared by organizations (row-level security,
                           │    restricted runtime user)
                           ├──► Blob Storage (a prefix per organization) and Key Vault
                           ├──► Document, media and accessibility workers (Container Apps)
                           ├──► Azure Communication Services (e-mail; data stored in Canada)
                           └──► Realizer control plane, api.realizer.io (app-only token):
                                plans, licenses, billing state, activity counts and dates
                                  └──► Stripe (paid plans)

 Realizer's Azure subscription, Canada Central; backups geo-replicated to Canada East
Regions and addresses
Each region is a self-contained deployment with its own address. Canada's is ca.app.realizer.io, with its API at api.ca.app.realizer.io. app.realizer.io is the global entry: sign-up first shows where the organization's data will be kept (today Canada) and then continues at the region's own address, and signing in there finds the person's region and opens it. The entry only forwards each visit, with the page address it was given, and stores nothing. Each organization stays in the region that registered it.
Sign-in, sessions and organizations
- Tokens never reach the page's script. The web host is a backend-for-frontend: it signs people in with a Realizer-owned app registration that accepts Microsoft work and school accounts of any tenant and personal Microsoft accounts, keeps their tokens in a server-side cache, and passes calls to the API with the person's token and the organization they chose. The browser holds only
__Host-cookies (Secure, HttpOnly, SameSite=Lax); every call needs a custom header, and no cross-origin access is offered. Each page is served with a fresh nonce for its Content-Security-Policy. - Access by membership. In hosted mode the API accepts only a delegated user token for AccessPoint, from the issuer of the token's own tenant. Access to an organization is decided by an active membership of it, never by the token's tenant: every call names an organization and is refused without a membership, with the same answer for an unknown organization and another organization's.
- Invitations. Only an Administrator's invitation creates a membership. An invitation link is stored only as a hash, works for 14 days and is matched only against the addresses the sign-in proves.
- Who can join. An organization can admit only work or school accounts of up to 10 named Microsoft tenants. A personal account never passes the list, and an Administrator cannot save a list that excludes their own account.
- Session limits. Each organization chooses how long a member may stay signed in without activity and the longest session, within the service's maximum of 120 minutes and 12 hours. Members are warned before either ends. Limits are enforced on the server for every call, and a session that ended cannot be replayed.
- Multi-factor authentication follows each member's Microsoft account: their own organization's Conditional Access for a work or school account, the person's own settings for a personal account. Who can join can limit an organization to its own tenants' accounts.
- No Microsoft 365 features. Hosted AccessPoint holds no Microsoft Graph permission and calls no Microsoft 365 service on an organization's behalf: no record capture from Microsoft 365, Teams notices, directory reconciliation or group-based roles, and people pickers search the organization's own members. Repository connectors are not offered.
Isolation by organization
Most organizations share one Azure SQL database, kept apart three ways: the application's unconditional tenant filter, automated guard tests on every place that filter could be bypassed, and SQL Server row-level security, which the hosted mode always runs on. The API connects as a restricted database user that cannot alter the security policy and cannot update or delete the audit ledger. Files sit under each organization's own prefix in storage. Caches, rate limits and e-mail budgets are counted per organization, and each organization has its own Lab mode training copy. Operations on a whole organization — exporting, moving it to a database of its own, or removing it — run only through an operator command in the service's own environment, never through a web endpoint, and each is recorded with the operator's name.
Edge, scanning and processing
- Azure Front Door with a web application firewall sits in front of the web host and the API, and both admit traffic only from Front Door. Front Door is a global Microsoft service that handles each request on its way in.
- Malware scanning. Microsoft Defender for Storage scans every uploaded file. A file found to be malicious cannot be previewed, downloaded or released, and a file still being scanned is held.
- Document, media and accessibility processing run in Azure Container Apps in Realizer's subscription in Canada Central, off the API, on AccessPoint's own document engine. A job carries only its own organization's file, the API applies each result only to that organization's record, and the workers never reach the database.
- Monitoring. Application Insights and request logs go to Realizer's Log Analytics workspace (30 days); Microsoft Defender for SQL runs in production, with alert rules for the service.
AI processing and consent
AI Assist is optional: an add-on on paid plans, and included in the trial.
- It sends the text a feature needs, which can include personal information from cases, to Azure OpenAI models that Realizer provisions in Canada, reached with a managed identity (no keys). Microsoft offers those models only as global deployments, so Microsoft may process prompts and answers in its other Azure regions.
- For that reason AI Assist stays off for each organization until one of its Administrators reads the statement in Settings and allows it. An Administrator can withdraw that permission at any time, and the AI features stop at once. If the statement changes materially, AI pauses until it is allowed again.
- What the AI produces is stored in the organization's region with everything else, and Microsoft does not use prompts or answers to train its models. Realizer chooses and manages the models in the hosted service.
- Text recognition (OCR), content search and transcription are processed in Canada and need no permission.
- As in the Microsoft 365 edition, every AI output is a suggestion for a person to check: drafts open in an editor and are never sent by themselves, and AI redaction suggestions apply only when a person accepts them.
Where hosted data lives
| Data | Where |
|---|---|
| Organizations' cases, documents, users and audit trail | Azure SQL and Blob Storage in Canada Central, under each organization's tenant ID |
| Backups | Database backups and stored files geo-replicated to Canada East, so they stay in Canada |
| E-mail content in transit | Azure Communication Services, with its data stored in Canada |
| Sign-in tokens and session records | A separate database of the web host, in the same region |
| Organizations (name and account contact), plans, licenses, billing state and activity counts | Realizer's control plane (api.realizer.io) — never case content, requester information or documents |
| Billing details and card data | Stripe — never AccessPoint or Realizer |
| Web traffic and sign-in | Azure Front Door and Microsoft sign-in, global services that handle each request on its way in |
| AI prompts and answers (once allowed) | Processed by Azure OpenAI global deployments, which may run in other Microsoft regions; results are stored in Canada |
Every message the hosted service sends — notices and letters to requestors included — goes through Azure Communication Services from Realizer's sending domain (accesspoint@notices.realizer.io, a subdomain kept apart from Realizer's own mail), carrying the organization's name and replies to the address the organization confirmed (a six-digit code goes to the address before it is used). Each organization has its own sending budgets, counted before a message leaves, so the shared sender can never be used to send mail in bulk.
License, control plane and releases
- Each organization has its own signed license, issued by Realizer's control plane with the same key and rules as a Microsoft 365 license and refreshed in the background. A revoked or lapsed license makes the organization read-only, as in the Microsoft 365 edition. A trial or a cancelled paid plan that ends moves the organization to the Free plan, where the registers that plan does not include are read-only. Nothing is deleted, and everything stays readable and exportable.
- The region calls Realizer; Realizer never calls in. The regional API reaches the control plane with an app-only token of its own managed identity. At most once a day the license refresh carries a summary of the organization's activity — dates and counts only, never a name, an address or case content.
- Releases are swapped in warm. Realizer releases each signed build after verifying its packages against the release key, deploys it to stopped staging slots, waits until they report healthy, swaps the API and then the web host, checks the result directly and through Front Door, and swaps back on any failure. Nobody is signed out by a release. Because the shared database is updated while the previous build still serves, a release may only add to the schema.
- Leaving. An organization's Administrators can download all of its data at any time from Settings > Subscription. Realizer deletes an organization that leaves only after a complete export is recorded.
What Realizer does and does not commit to
Realizer's operators hold Azure rights on the service's resources and carry the cloud provider's side of the controls: the deployment choices, network, logging, backup and recovery, releases and key management. The organization keeps what it controls inside the application — who it invites and their roles, Who can join, session limits, its e-mail settings, its retention periods and holds, and its own data and exports (see Customer Responsibilities).
Realizer keeps backups in Canada to recover the service after an incident; they are not a way to restore records an organization deleted. The service is provided without a promised uptime or recovery time unless a written agreement says otherwise (see the Hosted AccessPoint terms). ITSG-33 and PBMM are documented for AccessPoint for Microsoft 365 as a department deploys it (see the GC Security Controls Reference); Hosted AccessPoint has not been certified, assessed or authorized as a service by any third party.
Network and Firewall
These rules are for AccessPoint for Microsoft 365. In Hosted AccessPoint there is nothing to open in your own network: the browser talks over HTTPS 443 to app.realizer.io, the region's web host and API host, Microsoft sign-in and, when an Administrator manages billing, Stripe's hosted checkout and billing pages.
AccessPoint needs no custom ports and opens no inbound path into your own network. Every connection uses HTTPS on port 443, except the database connection (TDS on port 1433) between your web apps and your Azure SQL server. Staff reach AccessPoint through SharePoint and Teams; the only public-facing surface is the optional public portal.
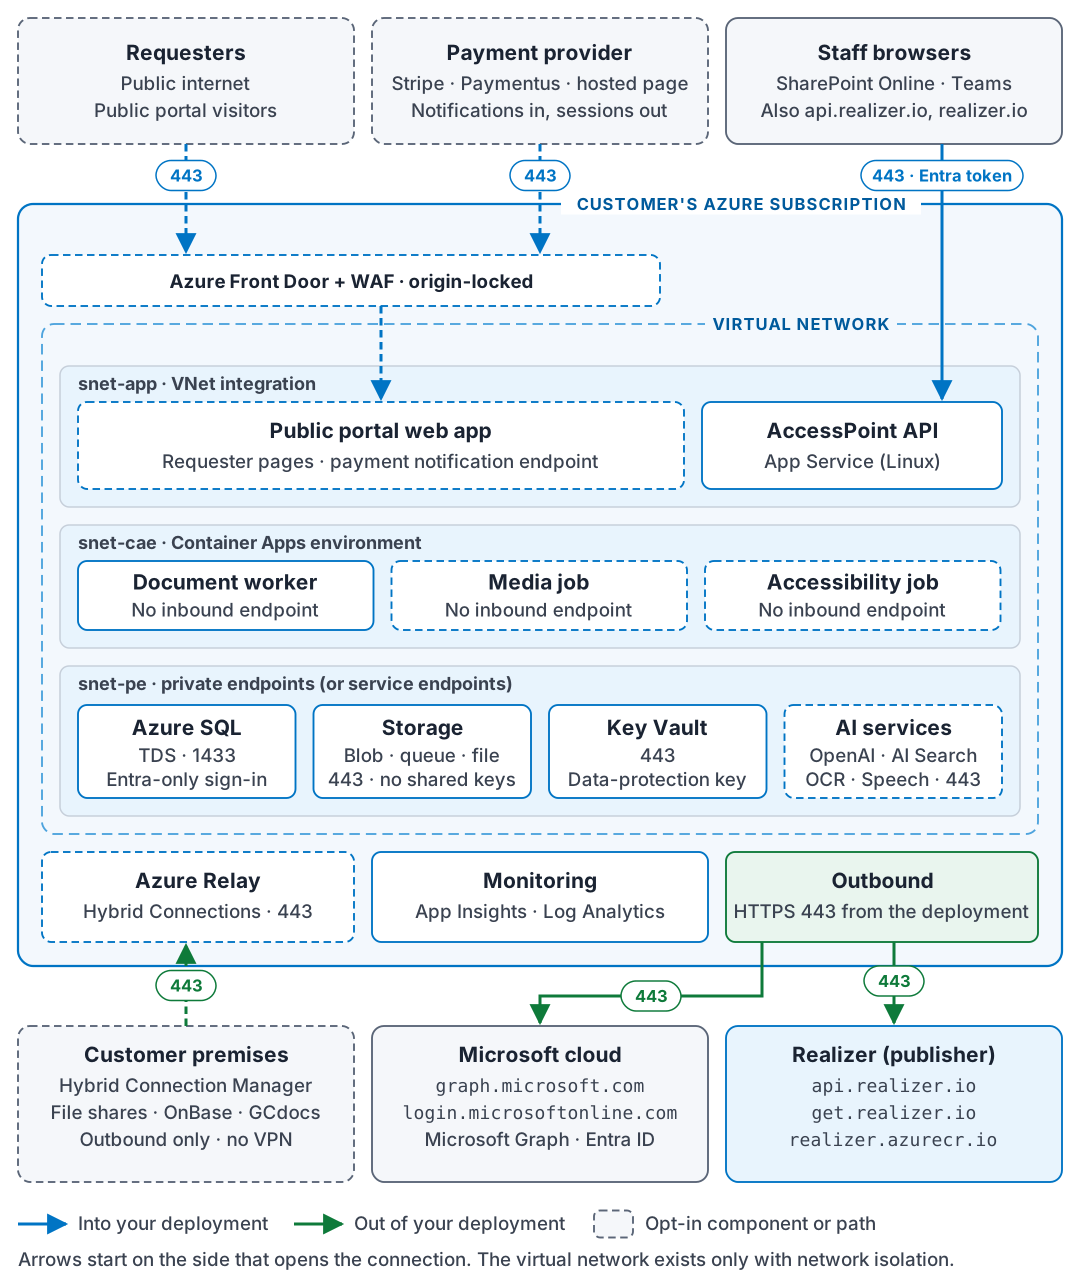
Arrows start on the side that opens the connection, which is the side a firewall rule has to allow. Dashed boxes are opt-in. The virtual network and its subnets exist only when network isolation is chosen at deployment (see Network Isolation Options); without it, the same services use public endpoints protected by Entra-only authentication, OAuth-only storage with shared keys disabled, and no anonymous blob access.
Inbound Connections
| Source | Destination | Port | Authentication |
|---|---|---|---|
| Staff browsers (SharePoint Online, Teams) | The AccessPoint API on App Service, or its Front Door endpoint with frontDoorForApi |
443 | Entra ID token on every call; cross-origin calls accepted only from SharePoint Online (*.sharepoint.com) |
| Requesters on the public internet (opt-in) | The public portal web app, or its Front Door endpoint and custom domain | 443 | Anonymous; an e-mailed one-time code opens every session; proof-of-work and per-address rate limits |
| Payment provider (opt-in) | The portal's notification endpoint, /api/pay/notify/{provider} |
443 | The provider's signature where the provider signs; otherwise the notification only triggers a status query. The API verifies every payment |
| Azure Front Door (opt-in) | The portal web app; with frontDoorForApi, the API too |
443 | Origin lock: each fronted web app admits only the AzureFrontDoor.Backend service tag carrying the profile's X-Azure-FDID |
| Package deployment | The API and portal web apps | 443 | Azure Resource Manager and the operator's Entra sign-in; publish profiles, SCM and FTP basic authentication are disabled |
No pipeline or Realizer system connects to your Azure SQL database: the API applies the schema itself at startup, and the server accepts Entra authentication only. Realizer has no access to your Azure resources, database or files.
Outbound Connections from the Deployment
If a firewall or proxy controls the deployment's outbound traffic, allow these destinations. Opt-in rows are needed only when that component is deployed or that feature is turned on.
| Destination | Port | From | Purpose |
|---|---|---|---|
| Your Azure SQL server | 1433 (TDS) | API; portal (opt-in) | Database queries; the portal's identity reaches only its own schema |
*.blob.core.windows.net, *.queue.core.windows.net |
443 | API, portal, workers, Speech | Documents, conversion jobs and worker queues in your own storage account |
*.vault.azure.net |
443 | API | Wrapping and unwrapping the data-protection keys (default on) |
graph.microsoft.com |
443 | API | E-mail, Teams notices in Direct mode, directory lookups, group membership checks, Copilot capture |
login.microsoftonline.com |
443 | API | Entra ID metadata and signing keys for validating every user's token |
| The Application Insights ingestion endpoint in the deployment's connection string | 443 | API, portal | Telemetry to your own Application Insights |
api.realizer.io |
443 | API | License validation, jurisdiction packs and the Teams relay (default mode). Only allow-listed Realizer hosts ever receive the API's managed-identity token |
get.realizer.io |
443 | Azure Resource Manager; the API on request | Release packages during deployment. Settings > Setup > Update now downloads and verifies one release, only when an administrator asks |
realizer.azurecr.io, or your own registry |
443 | Container Apps environment | Worker images (code only); mirror them into your own registry to remove this destination |
*.openai.azure.com, *.cognitiveservices.azure.com, *.search.windows.net (opt-in) |
443 | API | AI Assist, OCR, transcription and search, all in your own subscription |
*.servicebus.windows.net (opt-in) |
443 | API | The Hybrid Connections tunnel to on-premises connector hosts |
| Connector hosts you register (optional) | 443 or the registered port | API | Repository connector calls to registered addresses only; redirects are never followed |
api.stripe.com, the Paymentus host or your processor (opt-in) |
443 | API | Payment sessions, status queries, refunds and settlement |
| Linux package mirrors | 443 | API | The startup script installs system libraries and fonts in the background each time the API starts |
| Public web hosts named in e-mail records | 443 or 80 | API | Remote images in an e-mail being converted: at most 25 per message, public addresses only. This is the one plain-HTTP exception |
E-mail leaves through Microsoft Graph and your own Exchange Online, so it needs no SMTP relay, mail connector, SMTP AUTH, MX change or extra firewall rule (see Email Through Exchange Online).
Staff and Requester Browsers
If a web proxy or filter sits in front of staff devices, these destinations must be reachable over HTTPS 443, alongside SharePoint Online and Teams themselves:
| Destination | Used for |
|---|---|
The API's App Service host (*.azurewebsites.net) or its Front Door endpoint |
Every API call. The document viewer and editors load from the same host, with nothing from a CDN |
| Microsoft Graph and your own SharePoint and OneDrive | Capturing Microsoft 365 records with the user's own permissions |
api.realizer.io |
Finding your API's address, and routing the Teams personal tab |
realizer.io and www.realizer.io |
The in-app Help panel |
*.blob.core.windows.net (opt-in) |
Direct media playback through one-hour links, when the deployment sets sharePointOrigin |
Requesters' browsers (opt-in portal) reach the portal's host, the payment provider's hosted page, and *.blob.core.windows.net for secure-delivery downloads: single-file, read-only links that bypass Front Door. Under network isolation the portal streams the file itself instead.
On-Premises Records Systems
Repository connectors reach records systems on your premises, such as network file shares, Hyland OnBase and OpenText Content Server, through Azure Relay Hybrid Connections. The Hybrid Connection Manager, installed on a host in your network, connects out to Azure Relay (*.servicebus.windows.net) on port 443 and forwards the tunnelled traffic to the configured host:port. No inbound firewall rule and no VPN are needed. The API calls connectors with its managed-identity token; browsers never call a connector, and Realizer never sees connector traffic.
Network Isolation Options
By default the template deploys public endpoints protected by Entra-only authentication, OAuth-only storage with shared keys disabled, and no anonymous blob access. The template also offers a private network, best chosen at initial deployment because a Container Apps environment cannot join a virtual network after it is created:
| Option | What it does |
|---|---|
Service endpoints (deployNetworkIsolation=true) |
Creates a virtual network. The API and the portal join snet-app through regional VNet integration, with all their outbound traffic routed through it, and the Container Apps environment joins snet-cae. SQL, storage and Key Vault admit only those subnets through service endpoints: their public endpoints remain but accept nothing else. Azure OpenAI, Document Intelligence and Speech admit only the app subnet the same way; AI Search takes no service endpoint and stays public with Entra sign-in only (keys disabled). The portal streams deliveries itself, because a requester's browser cannot reach a storage link |
Private endpoints (networkIsolationMode=PrivateEndpoints) |
Replaces the service endpoints with private endpoints in snet-pe for SQL, storage (blob, queue and file), Key Vault and every deployed AI service, with privatelink DNS zones linked to the virtual network and public network access turned off on each. One exception: when Speech or Defender for Storage is deployed, the documents storage account keeps a deny-all firewalled endpoint that admits only trusted Azure services and the Speech account, because Speech batch transcription reads audio through the trusted-service exception |
Front Door and WAF (deployFrontDoor, frontDoorForApi) |
Managed TLS on the portal's custom domain and a web application firewall with per-client rate limits and a dot-segment block (on Premium, managed rule sets and bot protection too), in front of the portal and optionally the API. Each fronted web app is locked to the profile |
Defender for App Service (enableDefenderForAppService) |
Traffic- and sandbox-level threat detection for the API and portal web apps (a subscription-wide plan) |
Beyond the template, you can add inbound private endpoints for the API and portal web apps, Network Security Groups on the integration subnets, and a SQL firewall restricted to the App Service's outbound addresses (network isolation already restricts it to the virtual network). Front Door, WAF, App Service and blob logs go to your Log Analytics workspace by default; send a copy to a SIEM or Event Hubs with diagnostic settings of your own.
What Is Reachable from the Internet
- The public portal (opt-in) is the only public-facing surface. Its JSON routes send no CORS headers and require a custom header on every change, so only its own pages can call them; the payment notification endpoint is the only route a third party posts to.
- The API is publicly routable, or reachable only through Front Door with
frontDoorForApi, but every call needs an Entra ID token, cross-origin calls are accepted only from SharePoint Online, and its host name appears on no public page. The portal never calls it: the two exchange work through tables in the database. - Rate limits apply per user (1,200 requests a minute by default) and per address for anonymous calls, with HTTP 429 and
Retry-Afterwhen exceeded. - The workers have no inbound endpoint at all; they take their work from storage queues.
Email Through Exchange Online
In AccessPoint for Microsoft 365, AccessPoint sends e-mail through your organization's own Exchange Online with Microsoft Graph sendMail (Hosted AccessPoint uses Azure Communication Services instead — see E-mail under Hosted AccessPoint). There is no SMTP relay, mail connector, SMTP AUTH or MX change. A message leaves as an ordinary message from your own mailbox, so your domain's SPF, DKIM and DMARC apply, as do the sender mailbox's normal Exchange Online sending limits. AccessPoint sends notifications, correspondence and automatic acknowledgement letters, public-portal verification codes and notices, and security advisories to your own contacts.
| Mailbox | Sends |
|---|---|
The shared sender mailbox (for example accesspoint@contoso.com, set in Settings > Setup) |
Notifications, portal codes and notices, and advisory notices; letters and acknowledgements when chosen |
| An officer's own mailbox | Correspondence the officer sends, which is the composer's default |
| An intake mailbox (listed in Settings > Organization) | Automatic acknowledgements and letters sent from that inbox. Listing a mailbox grants nothing: each user still needs Exchange Full Access to open it |
What it needs. The shared sender mailbox; Mail.Send and User.ReadBasic.All granted with administrator consent to AccessPoint's Microsoft 365 identity (the App Service's managed identity, or on a split tenant the Microsoft 365 app registration), by the Finish Setup page or the deployment script, followed by a restart of the API; and e-mail notifications switched on in Settings > Setup.
Restricting Mail.Send (recommended). An application Mail.Send grant can send as any mailbox in the tenant until Exchange Online restricts it. An Exchange Online application access policy scoped to a mail-enabled security group limits it to the mailboxes in that group, so the group must hold every mailbox AccessPoint sends as: the shared sender, each intake mailbox used to send letters or acknowledgements, and the mailbox of every officer who sends correspondence from their own mailbox. Exchange refuses a send as a mailbox outside the group. The steps are in the Deployment Guide.
Never requested. Delegated Mail.Send, Mail.ReadWrite, any application permission that reads mail, full_access_as_app, EWS, IMAP, POP and SMTP AUTH. The API never reads a mailbox. Reading happens only in the user's browser, with that user's own delegated access, which Exchange enforces.
Encryption
In Transit
| Connection | Protocol | Minimum TLS |
|---|---|---|
| Browser → App Service | HTTPS (enforced, httpsOnly: true) |
TLS 1.3 |
| SPFx → App Service | HTTPS (enforced by SharePoint context) | TLS 1.3 |
| App Service → Azure SQL | TDS with encryption (Encrypt=True) |
TLS 1.2+ |
| App Service → Blob Storage | HTTPS (managed identity) | TLS 1.2+ |
| App Service → Microsoft Graph | HTTPS | TLS 1.2+ |
The App Service enforces TLS 1.3 as its minimum at the front door (TLS 1.0/1.1/1.2 rejected); outbound connections to Azure backend services negotiate TLS 1.2 or higher.
At Rest
| Data Store | Encryption | Key Management |
|---|---|---|
| Azure SQL Database | Transparent Data Encryption (TDE) | Microsoft-managed keys (default) or a customer-managed key in Key Vault, added by the customer after deployment; template upgrades keep it |
| Azure Blob Storage | Storage Service Encryption (SSE), AES-256 | Microsoft-managed keys (default) or a customer-managed key, named at deployment or added afterwards; every later template deployment keeps it (since 2.5.0). Storage queues stay on Microsoft-managed keys |
| Data-protection key ring | Each new key is wrapped with an RSA-3072 key in Key Vault (on by default) | Key Vault with RBAC, soft delete and purge protection; only the API identity may wrap and unwrap, and every use is logged to Log Analytics |
| Application Insights | Platform encryption | Microsoft-managed keys |
Application-Level
| Feature | Mechanism |
|---|---|
| Document viewer tokens | ASP.NET Core Data Protection (WOPI-style token, 15-minute TTL, tenant cross-check on every anonymous viewer call) |
| Attestation e-signatures | SHA-256 hash of signatory and timestamp stored in audit fields |
| Connector and payment-provider secrets | Encrypted under the data-protection key ring, which is wrapped by Key Vault |
| Requestor e-mail addresses on the portal | Encrypted with a public key; the private key is held only by the API. Verification codes and session tokens are stored only as hashes |
Privacy by Design
AccessPoint implements structural privacy controls that are enforced at the API layer, not only in the UI.
PII Filter Middleware
A response-level middleware intercepts all JSON responses and strips PII fields for any caller who does not hold the view-requestor-PII permission (Custodians, Contributors, Readers, Reviewers, and Advisors never hold it), server-side, regardless of what the client requests. Fields stripped: requestorName, requestorEmail, requestorPhone, requestorAddress, subjectName, subjectDateOfBirth, plus representative identity/contact fields and identity-verification notes.
Notification PII Blanking
When notifications are sent to Custodians or Contributors, requestor PII is replaced with placeholder text in the notification content itself — even if the notification template includes PII merge fields.
Custodian / Contributor Isolation
- Custodians see only their assigned requests and work from sanitized instructions
- Contributors see only their assigned tasks
- Neither role can search, browse, or access requests outside their scope
Logging, Monitoring, and Audit
Application Insights
All API telemetry is sent to the customer's Application Insights instance:
| Signal | What Is Captured |
|---|---|
| Request traces | HTTP method, path, status code, duration, correlation ID |
| Dependency tracking | SQL queries, Blob operations, Graph API calls (duration, success/failure) |
| Exceptions | Unhandled exceptions with stack traces |
| Custom metrics | Request processing times, document conversion durations, media processing timings |
Audit Trail
AccessPoint maintains a comprehensive audit trail in the AuditHistory table (Azure SQL), recording the entity type, entity ID, action (Create, Update, Delete, StatusChange), field name, old/new values, an optional change reason (captured on status transitions such as close and reopen), the authenticated user, and a UTC timestamp. Audit records are immutable — they cannot be modified or deleted through the API.
Hash-Chained Audit Ledger
In addition to the field-level audit trail, a tamper-evident, append-only AuditLedger (SHA-256 hash chain) records actions across all modules. Integrity can be verified server-side, and a court-ready case audit export (formerly "evidence package") can be generated for a request.
Optimistic Concurrency
High-contention entities (Requests, Documents, CustodianAssignments) each carry a SQL Server ROWVERSION concurrency token. The client echoes the row version on update; if another writer has changed the row in the interim, the save is rejected with HTTP 409 ("Concurrent edit detected") rather than silently overwriting.
Retention Purge Log
One RetentionService engine disposes of aged-out records across five registers — requests, assessments, incidents, complaints, and standalone privacy risks — driven by a per-type RetentionPeriodMonths + RetentionStartPoint (NULL = keep indefinitely, the default). Records that must not age out are excluded by construction (an In Effect assessment, an Accepted risk, a risk anchored to a case), and an expired record another open case still depends on is refused server-side; eligibility is re-evaluated at purge time. When a record is purged the engine deletes document blobs, converted PDFs, annotations, and export packages from Blob Storage in addition to the database records. The RetentionPurgeLog records what was deleted, when, and by whom — EntityName identifies which register it came from, alongside a snapshot of its number, type, close date, and document count — a compliance-grade trail that survives the data removal and is itself never purged.
Log Analytics and Alerts
Application Insights is backed by a Log Analytics workspace with configurable retention (default 90 days; configurable 30–730 days). Data can be exported to Microsoft Sentinel or an existing SIEM. The Bicep deployment includes two default metric alerts on the App Service:
| Alert | Severity | Condition | Window |
|---|---|---|---|
| Server Errors | 2 (Warning) | HTTP 5xx count > 5 | 5 minutes |
| High Latency | 3 (Informational) | Average response time > 5 seconds | 15 minutes |
When an alert email address is supplied at deployment, scheduled-query alerts for SQL authentication failures, media job failures, and a media queue stall are created alongside them. Customers can customize thresholds and add action groups (email, SMS, webhook) in the Azure Portal.
Resource logs for the API and portal web apps, the Front Door profile (when deployed) and the documents storage account's blob operations, as well as the Key Vault audit log, are sent to the same workspace by default. When an alert address is supplied, a further alert rule fires on any mismatch or write failure of the audit-ledger anchors.
Zero Trust Alignment
This section maps AccessPoint for Microsoft 365. AccessPoint is designed on zero-trust principles. No request is trusted because of the network it comes from, every request is authenticated and authorized before it reaches data, and each component holds only the access its own job needs. Because AccessPoint runs in your own Azure subscription and Microsoft 365 tenant, your Entra ID controls (Conditional Access, MFA, device compliance, sign-in risk) decide who can obtain a token for it in the first place.
The table maps the design to the seven tenets of NIST SP 800-207 §2.1, the standard we design against. It is a design mapping, not a certification. In Microsoft's terms, tenets 3, 4 and 6 are verify explicitly, tenet 3 is also least privilege, and tenets 2, 5 and 7 are assume breach.
| NIST SP 800-207 tenet | How AccessPoint meets it |
|---|---|
| 1. All data sources and computing services are resources | Every store and service (Azure SQL, Blob Storage and Queues, Key Vault, the AI services, the document worker, the media and accessibility jobs, the portal and repository connectors) is reached with an Entra identity and its own authorization, never because it sits in the same resource group or network. The public portal is treated as an untrusted edge: it touches only its own schema and containers and never calls the API, and the API never trusts a tenant id, storage path, verification result or key read from the portal's tables. |
| 2. All communication is secured regardless of network location | Every connection is encrypted: TLS 1.3 minimum on the API, TLS 1.2 on the portal, Front Door, SQL and Storage, HTTPS only with HSTS, and SQL with Encrypt=True. The default deployment relies on identity rather than network location; network isolation is defence in depth. The document worker has no inbound endpoint at all. See Network and Firewall. |
| 3. Access is granted per session, with least privilege | Entra access tokens are short-lived and audience-bound. Viewer, editor, media and download links carry purpose-bound encrypted tokens (15–60 minutes) re-checked on every use; blob download links are single-blob, read-only user-delegation links; every public-portal session needs a fresh e-mailed code. Each workload identity holds only what its job touches: the workers cannot reach SQL or the API, the portal's database user is limited to its own schema, storage shared keys and AI-service keys are disabled, SQL accepts Entra sign-in only, and Mail.Send can be limited to the mailboxes AccessPoint sends as. Custodians and Contributors never see requestor personal information, and being named senior official grants view access to that one case only. |
| 4. Access is decided by dynamic policy | Permissions are resolved on each request from roles, per-case relationships, dynamic case-matched roles, coverage delegations and Entra group membership, and checked against the object being accessed. A dynamic role fails closed when its rule can no longer be evaluated; when Microsoft Graph cannot be reached, group-based grants use the last observed membership for at most 24 hours by default and then fail closed. Device state and sign-in risk are your Conditional Access policies, evaluated by Entra before a token is issued. |
| 5. The integrity and security posture of assets is monitored | Release artifacts are signed, and the SharePoint package update is verified against a publisher key pinned in the API before anything installs; worker images can be pinned by digest. Defender for SQL is on by default, with a weekly vulnerability assessment; Defender for Storage malware scanning (a flagged file can never be previewed, downloaded or released) and Defender for App Service are options. The user's device is assessed by Intune and Conditional Access. |
| 6. Authentication and authorization are dynamic and strictly enforced before access | Only delegated user tokens carrying access_as_user are accepted. The issuer must be the token's own tenant's, each signing key may sign only for its own issuer, and an app-only token is refused. A state-changing call from a tenant the deployment does not serve is refused before any user record is created. Every write endpoint is permission-gated on the server; the UI hides what a person cannot do, but it is never the control. |
| 7. Information is collected and used to improve security posture | API, portal, Front Door, storage and Key Vault logs go to Application Insights and Log Analytics by default. With an alert address, alert rules cover SQL authentication failures, media job failures and queue stalls, and any mismatch or write failure of the audit-ledger anchors. Record changes are kept in the field-level audit trail, and actions across every module in the hash-chained audit ledger. |
Where your tenant and subscription complete it. AccessPoint is built to work under these controls of your own:
- Conditional Access with MFA (phishing-resistant where possible) and device compliance, applied to SharePoint, Teams and the AccessPoint enterprise application.
- Network isolation (
deployNetworkIsolation, withnetworkIsolationMode=PrivateEndpointsto turn public access off) and Front Door with a web application firewall in front of the API (frontDoorForApi). - The least-privilege SQL runtime (
sqlLeastPrivilegeRuntime), so the API connects as a restricted contained user instead ofdbo. - Worker image digests, so a container runs exactly the image that was released.
- Privileged Identity Management for the Azure and Entra roles that administer the deployment, and restricted blob data roles on the storage account.
- An Exchange Online application access policy limiting
Mail.Sendto the mailboxes AccessPoint sends as.
Good to know.
- A disabled or deleted Entra account cannot obtain a new token, but a token already issued stays valid until it expires (typically about an hour); AccessPoint does not take part in Continuous Access Evaluation. A change to a person's roles or Entra group membership takes effect within 5 minutes.
- The default deployment uses public endpoints, and the SQL server's firewall admits Azure services at the network layer; sign-in is still Entra-only. Network isolation and the least-privilege SQL runtime above close both, and inbound private endpoints for the API and the portal are yours to add.
Security Advisories and Incident Notification
When Realizer publishes a security advisory, or must tell an organization about a security incident that affects it, the notice reaches the organization through several independent channels. Two of them run through the organization's own AccessPoint deployment, using the security contacts it registers in the app. Realizer holds no list of a customer's security staff: those addresses stay in the customer's own database, the license call carries none of them, and the publisher has no copy. Advisories are read by AccessPoint 2.5.0 and later.
Registering contacts. In Settings > Notification contacts, an administrator registers who should be reached, one tab per kind (Security, Privacy and Operations), each with a notice language. A monitored role mailbox such as security@ is the right choice. An address receives nothing until someone holding it confirms it through a link that expires after 7 days. See Notification Contacts.
How an advisory reaches the deployment. Realizer publishes an advisory to every tenant or to named tenants, for the AccessPoint versions it affects. It travels inside the signed license token the deployment fetches every 24 hours and when the API starts, so a tampered or spoofed response cannot put a notice in front of anyone. The API reads advisories only from a token it has validated and keeps an advisory's link only when it is an https address on the publisher's allow-list.
What the deployment does with it.
A banner for administrators with the advisory's ID, title and summary, whether action is required, the version that fixes it and a link to the published advisory. Severity is shown in words as well as colour (SEV-1 Critical, SEV-2 High, SEV-3 Medium, SEV-4 Low).
An e-mail to the confirmed contacts, sent from the organization's own notification mailbox in each contact's own language, never from Realizer:
Contact kind Receives Security Every advisory Privacy SEV-1 and SEV-2 advisories that require action, as a prompt for the privacy office's own assessment, never as a statement that personal data was affected Operations No advisories (service notices only) Once per contact. Each contact is told once, however many days the advisory stays published. A failed send is retried at later refreshes, up to five attempts, and a send whose outcome could not be recorded is never repeated automatically.
A record of every notice in Settings > Notification contacts > Advisory notices (the advisory, recipient, language, outcome and time), plus one entry per fan-out in the hash-chained audit ledger, with counts but no addresses.
The e-mails carry no attachments, images or tracking, and no link except the advisory's own. A Realizer notice never asks anyone to sign in, grant consent or give a credential.
Channels outside the deployment. The in-app channels need the deployment to be running, and the incidents that matter most may be ones where it is not. For an incident that affects a specific organization (SEV-1 or SEV-2), Realizer uses these channels in order:
- The account contact, by e-mail, always first. The one address Realizer holds for each subscription, confirmed at activation and re-confirmed every year, is e-mailed from
security@realizer.io. It still works when the deployment is down or compromised. - A tenant-scoped advisory, which produces the banner and the contact e-mails above, in the organization's own languages and from its own mailbox.
- A note on the status page, hosted apart from the publisher platform, so a recipient can confirm a notice is genuine, and the public advisory (with an Atom feed) once the facts are public. Every notice carries an advisory or incident ID that can be checked there or in the banner.
- A telephone call to a known administrator for a SEV-1 when no acknowledgement has arrived within 24 hours.
Teams notifications are never used for a security notice: a security message in a Teams feed is indistinguishable from phishing.
What your organization does. Make the account contact a monitored role mailbox and tell Realizer (support@realizer.io) when it changes; register and confirm at least one security contact and keep the list current; keep e-mail notifications and the sender mailbox configured; and run AccessPoint 2.5.0 or later.
Hosted AccessPoint. Realizer operates the service, so the incident to report may be in the service itself. If Realizer confirms a security incident that has affected, or likely affected, an organization's data, it tells that organization's Administrators and its account contact by e-mail without undue delay, and no later than 48 hours after confirming it, as the Hosted AccessPoint terms set out. The account contact is the person who created the organization unless the organization asks Realizer to change it, so keep it current through support@realizer.io, and keep at least one active Administrator who reads AccessPoint's e-mail. Service events are posted on the status page.
Related Pages
- Deployment Guide — deploy and update AccessPoint, optional components, signed releases.
- GC Security Controls Reference — ITSG-33 control mapping.
- GC Privacy Impact Assessment — data flows and privacy analysis, including the hosted edition.
- Customer Responsibilities — what Realizer provides and what your organization is responsible for, in each edition.
- Security Controls — the security controls AccessPoint applies.
- Hosted AccessPoint terms — the terms of the hosted service.